Here’s another idea that came to me last night when I was doing my online banking: being a British expat in USA, and still having a couple of UK credit cards and a bank account, I use their online facilities a lot (for transferring money around, paying my credit cards etc.). I have a UK account with Barclays, and as such I use their PINsentry device every time I log into my online bank.
(As a side note, as far as I know other UK — in fact, European too — banks use a similar system too. HSBC have their own system which doubles into a key ring, NatWest has something similar and I don’t know for sure, but I bet that Lloyds TSB uses the same. In fact I’d be surprise if any other reputable bank in the UK doesn’t use a similar system!)
Anyway, point being is that Barclays requires the usage of this PINsentry device, which is ultimately a smart card reader — apart from knowing my account number and some personal details, to log into my online banking I need to have my Barclays debit card with me (physically) and the PINsentry reader; second step of validating my login requires me to put the debit card in the reader and type my PIN, if this is correct then the PINsentry device issues me with an 8-digit number which I then need to pass over to the website as a last validation step.
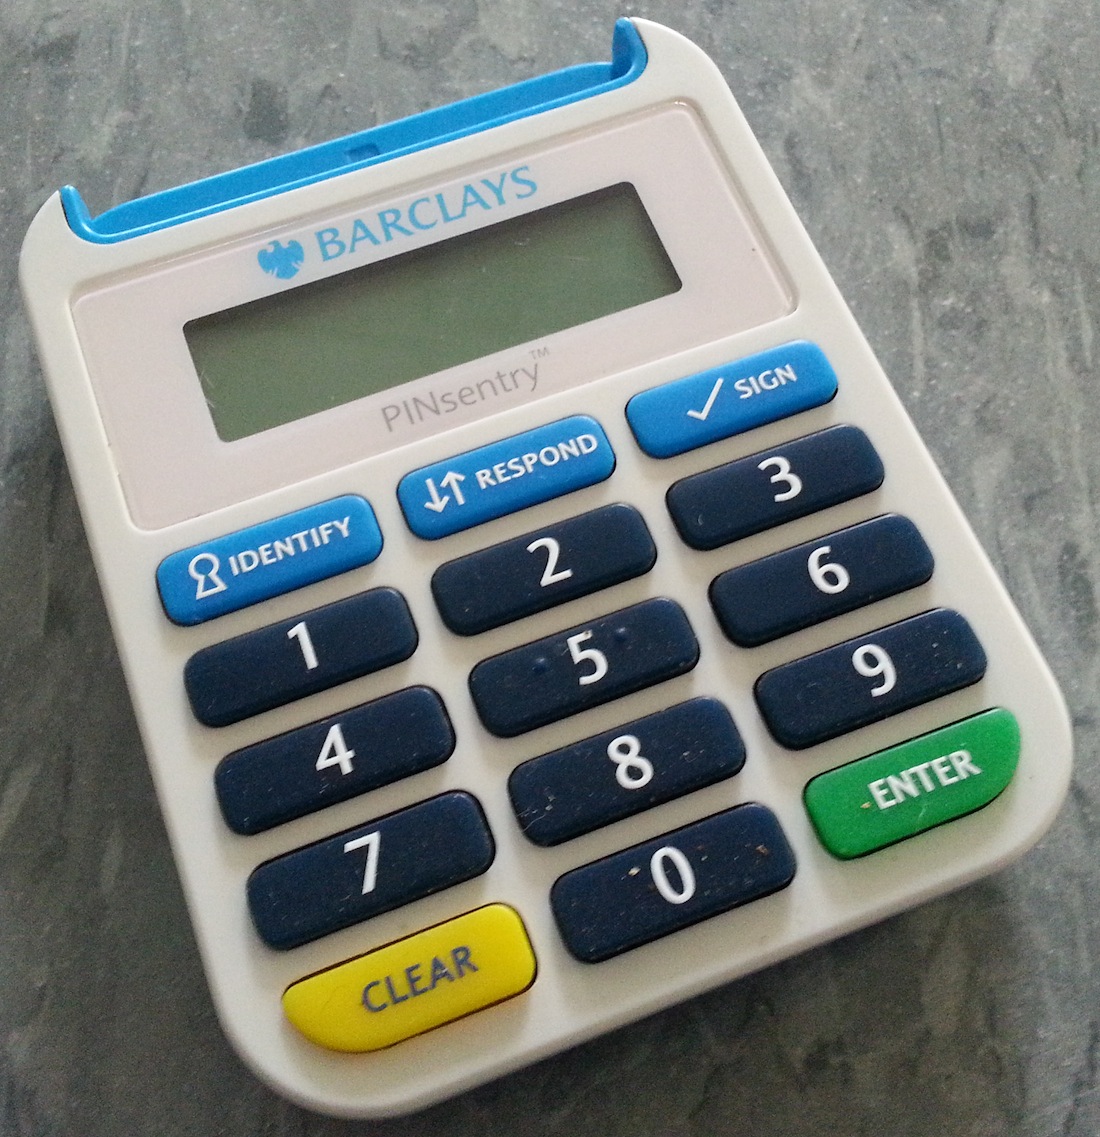
That is a great authentication mechanism because on top of knowing my personal details — which someone can get access to by intercepting my post — I have to have the card with me physically (which, again, someone can steal from me — I’m terrible with my wallet by the way) and also I need to know the PIN number. While the personal details and the card itself can be easily obtained, I keep my PIN pretty safe — to the point that I myself struggle sometimes remembering it 🙂 So I would argue that once these validation steps have been successfully passed, there is pretty much a certainty that the person sitting in front of the computer is me.
That is a big deal in the online world, I can assure you. No matter how strong your passwords are on any service/website you use, passwords can be stolen or broken into so that in itself doesn’t guarantee you for sure that the person using your service is who it should be. Even the 2-step validation employed by Google and Facebook doesn’t quite cut it for me — any “friend” of mine can easily get hold of my mobile for a few minutes and if they hacked my password they can end up “being me” on any of these services (minus Facebook which I can’t care about and don’t use :D).
Now since Barclays (and the other banks) have got this facility already in place and they have already rolled out their card readers and security systems, wouldn’t it be cool if each one of these banks offers you an “identity bank account” too? Simply put, in order to log into say Gmail, I have to use a similar mechanism: just know my email address, then pull out my bank card, the reader, put in the pin and voila, I’m logged into Gmail! With a near 100% certainty that the person who just logged in with my user name is me!
Ok, perhaps using Gmail for this is not the best example — but for instance I have an Amex Platinum card too, a Capital One card and another Visa credit card; for each one of these I have to remember username and password and an “online PIN” — none of which I consider “secure mechanisms”! However, if I could use a similar mechanism for my Amex (which by the way, like all the cards issued in Europe, has got a chip!) then I would feel happier and more secure that no one else can get to my online account. Same for Capital One and the others.
I don’t want though to end up using a separate card reader for each one of them — ideally I would like to use the Barclays one OR have these guys agree on a trusted 3rd party to issue readers for all types of cards. I am happy to declare — to either Barclays or the 3rd party — all the credit card types I have, such that if someone is trying to use say a HSBC credit card (which I don’t have!) with my reader then the device won’t work, but if I use any of my cards it will work just fine.
To me it would make sense to use the existing Barclays mechanism as a single sign-on into all these other services — it’s there, it’s already rolled out, there is no need for infrastructure updates/refreshes; however, I can see concerns being raised by the others as to why would the bank be the only one to issue these readers — and the politics of it is not my concern.
But if my bank could provide me an “identity bank account” where using my reader, my card and my PIN I can log into any other services I’m using, I think a lot of the online identity theft incurred by various online services nowadays would be diminished, or even eliminated. Imagine logging into your Barclays account using the PINsentry device, and from there on you have a button that logs you into facebook, gmail, Netflix whatever. From there on I think it would be just a small step to actually charge automatically for services too, right? I mean I’ll click on Netflix and the Barclays site will warn me: “you will be charge £10, and that will give you access for a period of 30 days if you continue” — all I have to do is click on “Accept” and money will be paid to Netflix by my bank and I will be safe in the knowledge that the transaction is carried out in between the bank and Netflix, securely so I won’t have to worry about my credit card details being safe or not either! Also, there won’t be any need for a subscription service, there’s no need for Netflix to hold on to my credit card details and bill me every month: if the only way I can get through to the service is my bank account, the bank software will talk to Netflix and enquire if there is a need for funds to be deposited in my Netflix account — if so, it will prompt me and go ahead and carry on the transaction — if not, it will just log me into Netflix and I can watch my movies as per normal!
All I have to have with me at any time is my debit card and my card reader — like I said, HSBC used to issue in the UK small card readers, which you can easily attach to your keyring. With the reader in your pocket, attached to your keys, and your card in your wallet always with you, you could argue you should be able to always log into any service you want — given that you have Internet connection and you can remember your PIN. And, on top of that, you can offload all the payment processing to where they should happen: inside the bank!
So what do you say, Barclays? Do-able? Or should I turn to HSBC? 🙂 lol